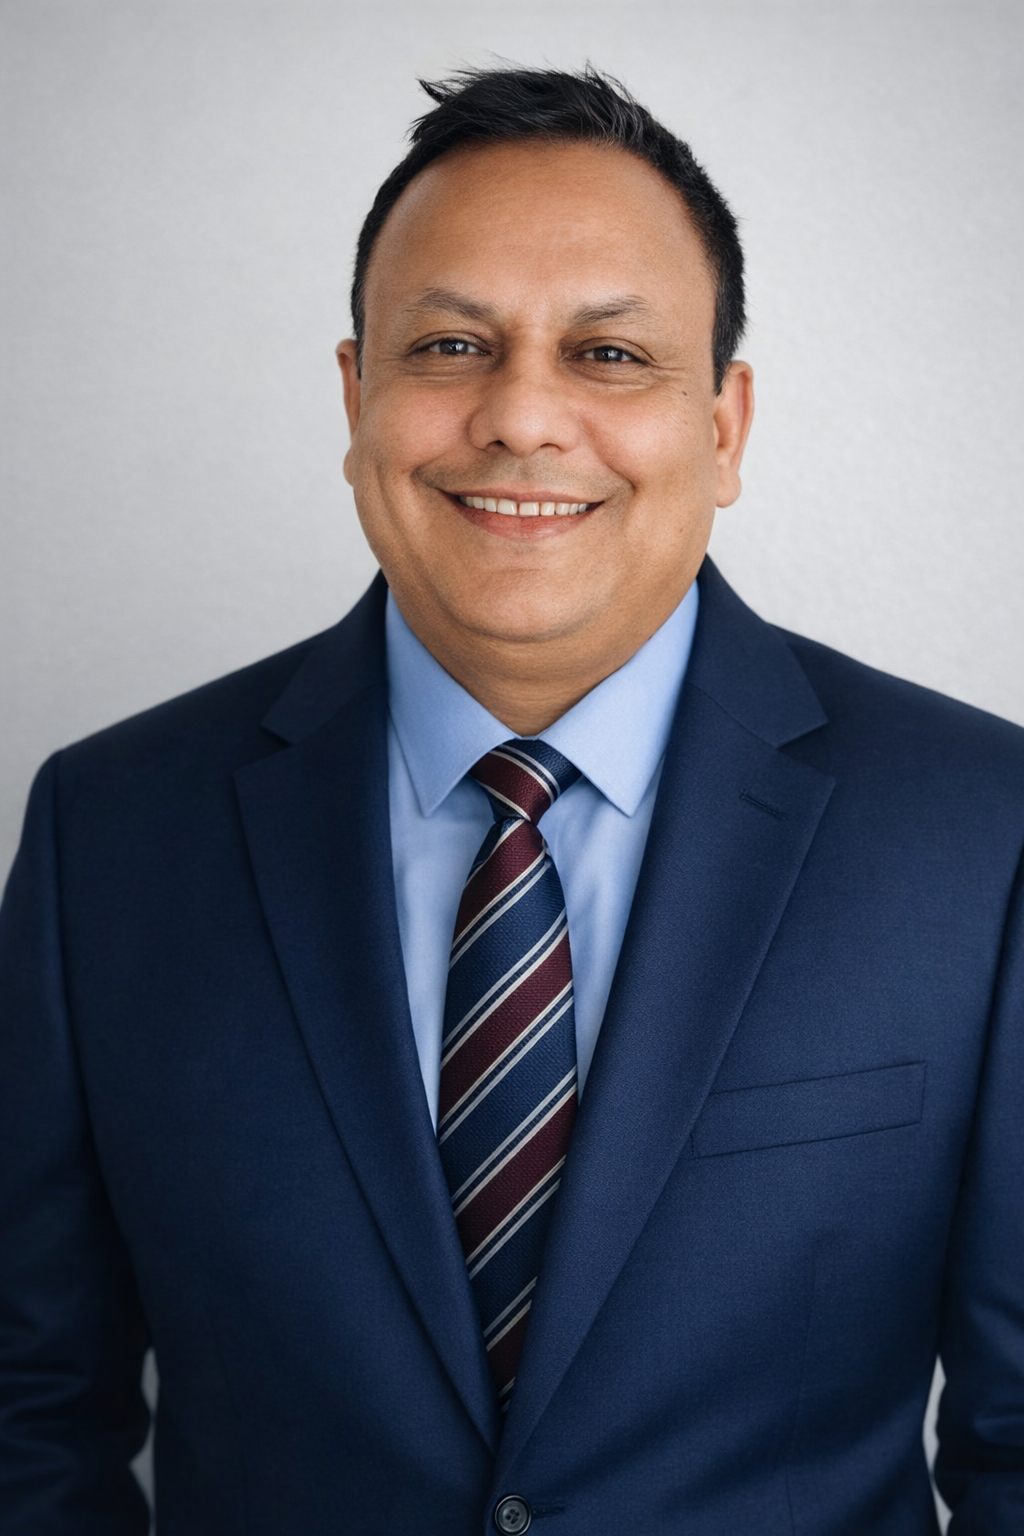
Kiran Regmi
SOC Analyst · Security Operations · Threat Detection
Cybersecurity professional with hands-on experience in SIEM monitoring (Splunk, QRadar), alert triage, phishing detection, threat intelligence, and incident investigation. Built and secured a production web platform with Cloudflare WAF, JWT auth, RBAC, audit logging, and a live global threat map.
"Portfolio demonstrates production-ready SOC workflows — not just labs."
Real Security Infrastructure — Live & Deployed
OPPORTUNITYISNOWHERE.
Global Threat Map
Real-time Cloudflare WAF events plotted on a D3.js world map. Blocked attacks, bot interceptions, and threat origins from actual firewall logs — live.
Security Posture
18 active security controls documented with decision rationale. NIST CSF 2.0 alignment, change log, and architecture decisions explained — interview ready.
SOC Interview Platform
145 curated SOC analyst interview questions across 10 domains. JWT-authenticated, RBAC-protected. Built as a real app, not a static page.
SOC Analyst Mindset
Tier-1 drives operational stability — reducing noise for Tier-2/3 and preventing delays in real threats. Every alert qualified properly saves senior analysts valuable time.
Strong shift handovers ensure 24/7 situational awareness with no dropped alerts. Clear documentation and escalation protocols maintain continuous security posture.
SOC Analyst Toolkit
Professional Certifications
9 Industry-Recognized Credentials · Click to view certificate
Featured SOC Projects
Secure Interview Platform
JWT Auth · RBAC · SOC Workflow
Production-grade platform demonstrating SOC investigation methodology with role-based access, audit logging, and documented escalation protocols.
AI-Driven SOC Automation
AI Assistant · Log Analysis · GRC
AI-powered tools to augment analyst workflows — log correlation, alert enrichment, and voice agent for scheduling, with human-in-the-loop decision authority.
SIEM Alert Investigation
QRadar · Threat Intel · IOCs
Hands-on SIEM investigation using QRadar and Splunk: directory traversal detection, multi-source threat intel enrichment, and escalation-ready reporting.
Active on GitHub
Building security tools, documenting SOC workflows, and contributing to cybersecurity projects.
View GitHub ProfileReady to discuss your security team needs?
Available immediately · Fort Worth, TX · Open to remote & hybrid roles